About Mark Darland
With over 23 years of experience in Information Technology, I have dedicated my career to protecting critical infrastructure through network security and strategic architecture planning.
Professional Experience
Network Stack Hardening
Throughout my career, I have focused on strengthening network infrastructure by implementing comprehensive security protocols, including Border Gateway Protocol (BGP) hardening, firewall optimization, and intrusion detection systems. My work has contributed to securing enterprise networks against evolving cyber threats.
Hybrid Deployment Security
I specialize in bridging on-premises infrastructure with cloud environments, ensuring seamless security integration across hybrid deployments. This includes designing secure connectivity solutions, implementing zero-trust architectures, and maintaining compliance across diverse technology stacks.
Security Architecture & Analysis
My approach to security architecture emphasizes defense in depth, least privilege access control, and continuous monitoring. I have experience conducting security assessments, developing incident response procedures, and implementing security frameworks aligned with industry best practices.
Comprehensive Security Approach
Local Area Network (LAN) Security
Implementing comprehensive LAN security through multilayered defense models incorporating physical, logical, and administrative controls. Expertise in network segmentation using VLANs, Access Control Lists (ACLs), and IEEE 802.1X authentication for identity-based access control. Deploying Dynamic ARP Inspection (DAI), IP Source Guard, and Port Security to defend against MAC flooding, ARP spoofing, and IP address forgery. Implementation of Next-Generation Firewalls (NGFWs) with Intrusion Detection and Prevention Systems (IDS/IPS) for deep packet inspection and application-layer filtering.
Cloud Infrastructure Security
Securing cloud environments through comprehensive Identity and Access Management (IAM), implementing least privilege principles, multi-factor authentication (MFA), and role-based access controls (RBAC). Building microsegmented architectures using virtual private clouds (VPCs) with restrictive security group and network ACL policies. Implementing Cloud Security Posture Management (CSPM) solutions for continuous monitoring of misconfigurations and compliance gaps. Utilizing Cloud Workload Protection Platforms (CWPP) to extend runtime protection to virtual machines, containers, and serverless functions.
Container Security & Orchestration
Implementing secure containerization strategies through image provenance and integrity verification. All container images undergo vulnerability scanning using industry-standard tools before deployment. Configuring Kubernetes Role-Based Access Control (RBAC) and Pod Security Policies to restrict administrative privileges and prevent privilege escalation. Runtime security monitoring detects deviations from normal operational patterns through continuous analysis of system calls, process behavior, and network traffic.
Zero Trust Architecture
Embracing Zero Trust Architecture (ZTA) principles across LAN, cloud, and container environments. Enforcing identity verification, continuous authentication, and microsegmentation regardless of location or device. Deploying Secure Access Service Edge (SASE) and Extended Detection and Response (XDR) platforms to correlate threats across networks, endpoints, and cloud workloads within a unified, adaptive security framework.
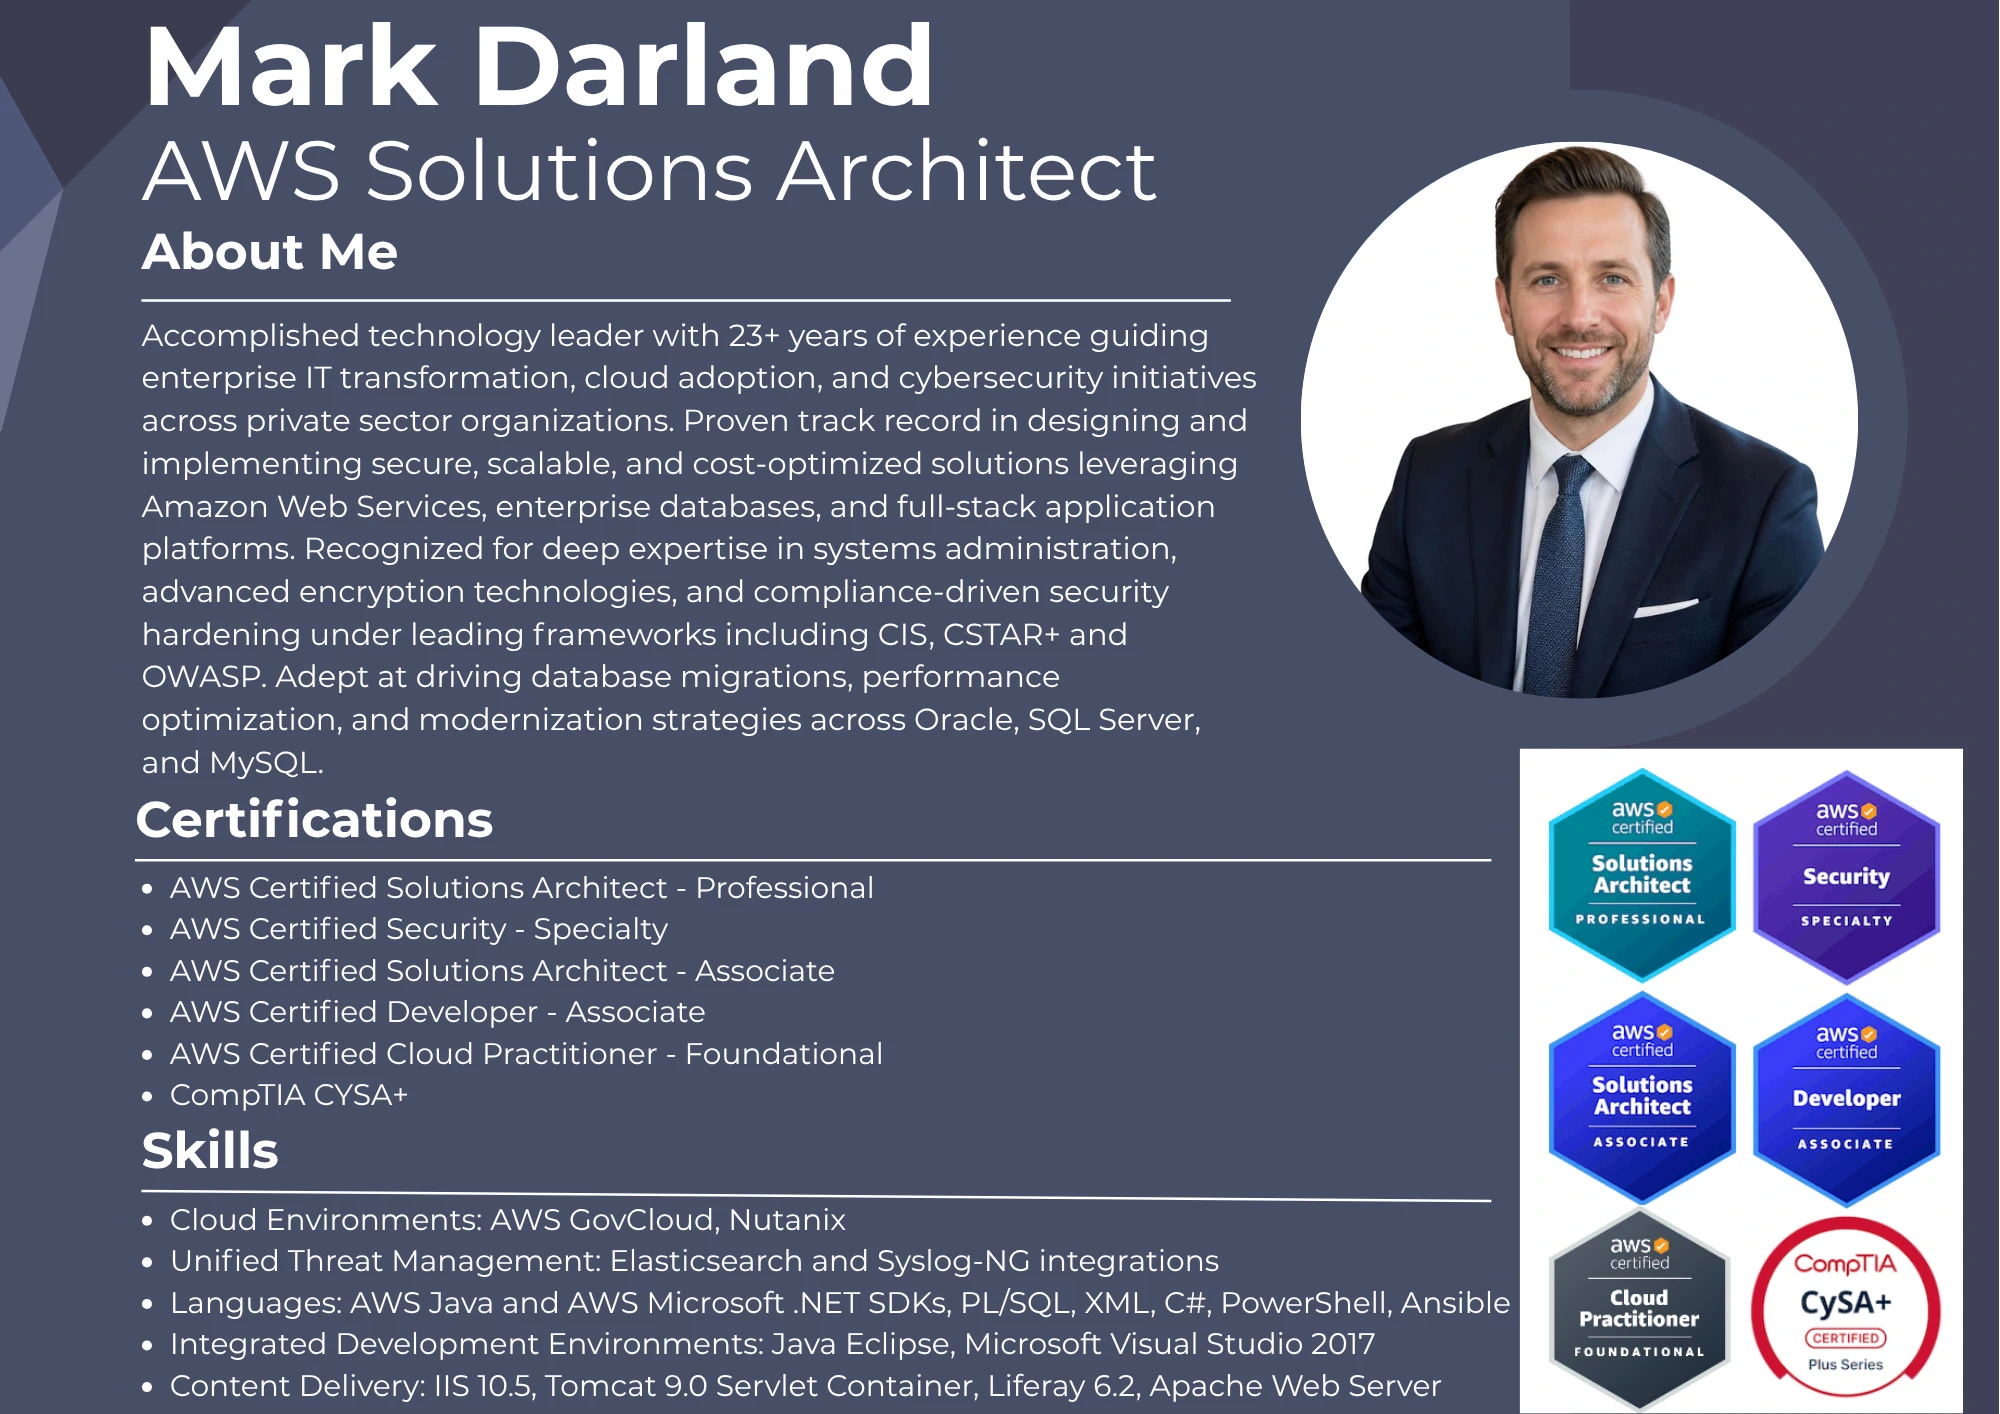
Certifications & Skills
AWS Solutions Architect
Professional Certification
Network Security
BGP & Stack Hardening
Hybrid Cloud Security
On-Premises Integration
Security Analysis
Threat Detection & Response
Connect
I am passionate about sharing knowledge and connecting with fellow professionals in the cybersecurity and IT infrastructure community. Feel free to reach out through any of the social platforms linked in the footer below.